Blog
Designing HIPAA-Compliant Data Pipelines for Multi-System Integration

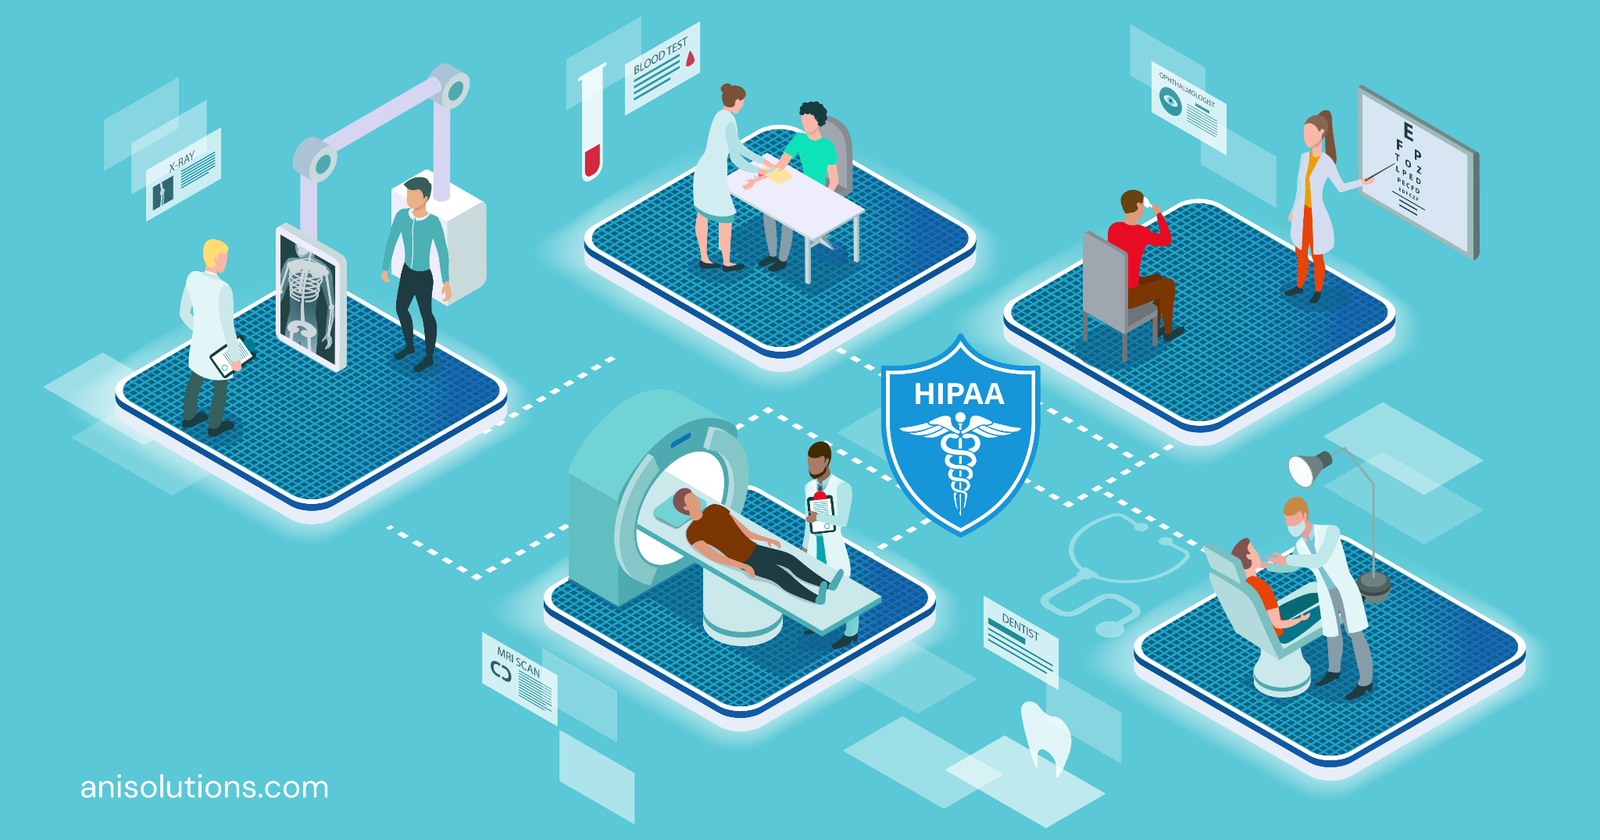
You may have heard this before that healthcare is the most attacked industry by cyber criminals. And the reason for this is the sensitive patient information, including the personal data, financial information, and insurance details.
However, in these attacks, the most vulnerable part is the data pipelines that transmit this Patient Health Information (PHI). In the past, the data pipelines were simple and far less than what it is in today’s interoperability, which connects multiple systems through healthcare data pipelines.
These integrations increase the attack surface with each connection, and this leads to an increase in data breaches. And the penalties are also quite high and can go up to $1 million, and that’s where HIPAA-compliant data pipelines come into the picture.
You need to follow a HIPAA framework to design data pipelines that move data securely between third-party platforms through secure APIs. That’s where HIPAA-compliant integration becomes critical.
In this blog, we will break down how you can design a secure, encrypted, and compliant system for smooth data transmission.
The Core Elements of a Secure Data Pipeline
If you strip it down, secure healthcare integrations come down to a few core principles. Miss any one of them, and the entire pipeline becomes fragile.
First, encryption isn’t negotiable. Data in transit should always be protected using TLS 1.2 or higher. Data at rest needs strong encryption like AES-256—across databases, storage systems, backups, and even message queues. If there’s a weak link anywhere, that’s exactly where attackers will look.
Next comes vendor accountability. Every system that touches PHI—cloud providers, integration platforms, analytics tools—needs a Business Associate Agreement. But too many organizations stop at signatures. A BAA doesn’t secure anything by itself. You need to validate that vendors are actually enforcing the controls they claim.
Access control is another common weak spot. Strong pipelines enforce least privilege access, meaning users and systems only get what they absolutely need. Add multi-factor authentication on top of that, and suddenly a large class of attacks becomes much harder to execute. Even service accounts—the ones people forget about—need tight permissions and regular credential rotation.
Then there’s de-identification. Not every use case requires identifiable data. For analytics or research, stripping identifiers using HIPAA-approved methods reduces risk without limiting value.
These aren’t advanced strategies—they’re fundamentals. But in healthcare data security, fundamentals are exactly where most failures begin.
Designing for Multi-System Integration
Securing a single system is manageable. Securing the connections between multiple systems—that’s where things get complicated fast.
Most healthcare environments today rely on a mix of legacy EHRs, modern cloud platforms, third-party apps, and analytics tools. These systems weren’t built to work together securely by default. So the responsibility shifts to how you design the integration layer.
Legacy systems are usually the biggest constraint. Many don’t support modern authentication or security protocols. That’s why integration layers—like API gateways or middleware—become critical. They act as a security buffer, enforcing standards like OAuth 2.0, handling encryption, and controlling access before requests ever reach the core system.
APIs play a central role here. Well-designed, secure healthcare APIs ensure that every data request is authenticated, authorized, and limited in scope. OAuth 2.0 helps enforce that by issuing scoped tokens instead of exposing full system access. Done right, this drastically reduces the risk of overexposure.
But security isn’t just about controlling access—it’s about visibility. Every interaction between systems should be logged. Audit trails need to capture who accessed what, when, and from where. Not just for compliance, but for real-world incident detection.
There’s always tension between interoperability and privacy. You need to share data—but only what’s necessary, and only with the right controls in place. That balance is what defines a strong HIPAA data integration strategy.
Common Risks & How to Avoid Them
Most healthcare security failures don’t come from sophisticated attacks. They come from small oversights that quietly turn into big problems.
One of the most common issues is PHI leaking into places it shouldn’t—especially logs. During debugging, it’s easy for developers to capture patient names, IDs, or clinical data in log files. Those logs often sit in less secure environments, with broader access than production systems. The fix is simple but often ignored: never log sensitive data in plain text, and always mask or scrub PHI before anything gets recorded.
Then there are “shadow integrations.” These are unofficial connections—like a spreadsheet pulling data from an API or a third-party tool set up without IT approval. They usually start with good intentions but end up creating unmonitored data flows, often without encryption, access controls, or proper agreements in place.
Outdated systems are another persistent risk. Legacy infrastructure with known vulnerabilities becomes an easy entry point if it isn’t regularly patched or assessed. Many enforcement actions trace back to something basic that was left unaddressed for too long.
Avoiding these issues isn’t about adding more tools—it’s about tightening discipline:
- Control what gets logged
- Track every integration
- Keep systems updated
Because in healthcare data security, it’s rarely one big failure—it’s a chain of small ones that gets exploited.
Making Compliance Part of Daily Operations
The biggest mistake organizations make with HIPAA-compliant integration isn’t a lack of effort—it’s treating compliance like a one-time setup.
Security doesn’t fail because controls were never implemented. It fails because they weren’t maintained.
Real compliance shows up in daily operations. It starts with regular risk assessments—not just annual exercises, but something tied to change. Every new integration, vendor, or system update should trigger a review. If your environment evolves but your risk posture doesn’t, gaps are inevitable.
Testing is another area where things slip. Vulnerability scans and penetration tests shouldn’t happen only after an incident or before an audit. They need to run on a defined cadence, catching weaknesses before they’re exploited.
Then there’s the human factor. Most security incidents still involve some form of human error—phishing clicks, weak passwords, or misconfigured access. Training helps, but only if it’s practical and repeated. One annual module isn’t enough to change behavior.
What ties all of this together is monitoring. Continuous visibility into access patterns, authentication failures, and unusual data activity gives teams a chance to respond early. Without it, issues often go unnoticed until they escalate.
Compliance isn’t documentation—it’s behavior. And in healthcare data security, consistent behavior is what actually keeps systems secure.
The Future of Secure Healthcare Integration
The traditional approach—trust everything inside the network—doesn’t hold up anymore. Data now flows across cloud platforms, remote devices, third-party apps, and distributed teams. That’s why zero-trust architecture is quickly becoming the standard. Every request is verified, every access is scoped, and nothing is trusted by default—no matter where it originates.
At the same time, integration itself is shifting. Legacy interface engines are giving way to cloud-native, API-driven pipelines. These systems are more scalable and flexible, but they also move the security perimeter. It’s no longer about protecting a network boundary—it’s about securing identities, APIs, and data flows across environments.
AI is starting to play a role here as well—not in replacing security teams, but in extending their visibility. With dozens (or hundreds) of integrations running simultaneously, manual monitoring doesn’t scale. AI-driven systems can baseline normal behavior and flag anomalies—unusual access patterns, unexpected data volumes, or activity that doesn’t fit historical trends.
Regulations are also catching up. Expectations around encryption, access control, and continuous monitoring are tightening, pushing organizations toward stronger, more proactive security practices.
The direction is clear: secure healthcare APIs, identity-driven access, and continuous verification will define the next generation of HIPAA-compliant integration.
Conclusion: Building Secure & Scalable Data Pipelines
In a nutshell, exchanging data securely is not an option but an essential requirement in modern healthcare. With increased interoperability and complexity of information exchange, this leads to every connection, API, and data should be secure data pipelines.
This is where HIPAA-compliant integration makes it safe to exchange data across systems and reduces the risk of heavy penalties. But when you have encrypted data pipelines, audits, and governance policies, you can easily exchange patient data without worrying about data breaches.
So, if you want a secure healthcare data pipeline, then explore A&I Solutions to see how we have helped other healthcare organizations.
FAQs
- What is HIPAA-compliant integration in healthcare?
HIPAA compliant integration refers to securely connecting healthcare systems—like EHRs, billing platforms, and APIs—while meeting HIPAA Privacy and Security Rule requirements. It ensures patient data (PHI) is protected during transmission, processing, and storage through encryption, access controls, audit logs, and strict data-sharing policies.
- What are the key requirements for secure healthcare data pipelines?
Secure healthcare data pipelines require strong encryption (TLS 1.2+ in transit, AES-256 at rest), strict access controls, multi-factor authentication, audit logging, and vendor compliance through BAAs. They must also enforce least privilege access and ensure data integrity across all connected systems and integrations.
- How do BAAs impact healthcare data integration?
Business Associate Agreements (BAAs) legally define how vendors handle protected health information. In healthcare integration, they ensure third parties follow HIPAA standards for security, breach reporting, and data use. Without a BAA, sharing PHI with vendors creates compliance risks and potential legal penalties.
- How can organizations prevent PHI exposure in data pipelines?
Organizations can prevent PHI exposure by avoiding sensitive data in logs, masking identifiers, encrypting all data flows, and restricting access through least privilege policies. Regular audits, secure API design, and monitoring unusual activity also help detect and prevent unauthorized data exposure early.
- What are common security risks in multi-system healthcare integration?
Common risks include unsecured APIs, outdated systems, shadow integrations, weak access controls, and PHI leakage in logs. Integration gaps between legacy and modern systems also create vulnerabilities. Without proper monitoring and governance, these risks can lead to data breaches and compliance violations.
- How does encryption protect healthcare data?
Encryption protects healthcare data by converting it into unreadable formats during transmission and storage. Even if intercepted, encrypted data cannot be accessed without proper keys. Using TLS for data in transit and AES-256 for data at rest ensures strong protection against unauthorized access.
- What role does IAM play in HIPAA compliance?
Identity and Access Management (IAM) ensures only authorized users and systems can access PHI. It enforces least privilege access, multi-factor authentication, and role-based permissions. Proper IAM reduces insider threats, prevents unauthorized access, and is a critical requirement for maintaining HIPAA compliance.
- How can healthcare organizations maintain ongoing compliance?
Ongoing compliance requires regular risk assessments, continuous monitoring, staff training, and routine security testing. Organizations must update systems, review access controls, and evaluate vendors consistently. Compliance should be embedded into daily operations, not treated as a one-time checklist or annual activity.

A procurement manager at a mid-sized manufacturer signs off on a new packaging supplier. The quote is competitive, the samples are good, and the decision looks sound. Eight months later, an internal review notices that the supplier’s operations director is the manager’s brother-in-law.
The manager never hid the relationship. Nobody ever asked. The annual declaration form he completed two years earlier covered shareholdings and second jobs, and at the time his brother-in-law worked somewhere else entirely.
Most conflicts of interest look like this. They are rarely schemes. They are ordinary relationships and interests that shift over time, meeting a disclosure process that only looks once a year, at a single point, with the same questions for everyone.
A Conflict Is Not A Wrongdoing
A conflict of interest exists when someone’s personal interests could influence, or appear to influence, decisions they make at work. Having one is not misconduct. Failing to declare it, or continuing to make decisions affected by it, is where the problems begin.
The distinction matters because it shapes how people respond. If staff believe that admitting a conflict will be treated as a confession, they will declare as little as possible. If they see disclosure as a routine part of working life, followed by sensible arrangements such as stepping back from a particular decision, they are far more likely to be open.
Organisations that handle conflicts well tend to treat declarations as useful information rather than evidence against the person making them.
Where Conflicts Usually Hide
Financial interests are the obvious category: shares in a supplier, a stake in a competitor, or an investment in a business the organisation deals with. They are also the type most forms are designed to catch.
Family relationships are harder. A partner working for a customer, a sibling running a contractor, or a relative applying for a job in the same department can all create conflicts that the employee may not think to mention unless asked directly.
Outside employment and roles raise similar issues. Consulting work, a seat on another company’s board, or a part-time role with a charity that receives funding from the employer can all overlap with someone’s main job.
Gifts and hospitality from business contacts, and political or government relationships, round out the common categories. Each carries different risks depending on who receives them and what decisions that person makes.
Why One Form For Everyone Falls Short
The traditional approach sends the same declaration form to every employee once a year. It is simple to run, and it creates a record that disclosures were requested. It also has clear weaknesses.
A warehouse operative and a head of procurement face very different conflict risks. Giving them identical questions means the form is either too detailed for most staff or too shallow for the people whose decisions carry real financial weight.
Volume is another problem. In a large organisation, hundreds of declarations arrive in a short window. Most are routine. A small number deserve close attention. When everything lands in the same queue, reviewers spend their time on the routine ones while the significant disclosures wait.
Annual timing is the third weakness. People change roles, relatives change jobs, and new suppliers are appointed throughout the year. A snapshot taken every twelve months can be out of date within weeks.
Asking Better Questions
Many organisations now tailor declarations to the role. Senior leaders and directors receive questions about board positions and significant financial interests. Procurement staff are asked specifically about relationships with suppliers. Managers are asked about connections to people in their reporting line. Everyone else receives a shorter baseline form.
Adaptive questioning helps further. When someone answers yes to having a relationship with a supplier, follow-up questions appear asking for details. When an answer crosses a set threshold, such as a gift above a certain value, the declaration can be flagged for prompt review. Staff with nothing to declare move through quickly, and those with something relevant are guided to provide what reviewers actually need.
Tracking Change, Not Just Status
A single year’s declarations show what people have disclosed. Comparing years shows what has changed, which is often more revealing.
When last year’s answers are carried forward, employees can confirm that nothing has changed or update what has. Reviewers can then see new conflicts, modified ones, and those that have been resolved, rather than reading every declaration from scratch. Patterns that build gradually become visible, and the organisation has a full history if it ever needs to show how a particular conflict was handled.
Moving From Policing To Guidance
The most useful shift many organisations make is introducing pre-clearance. An employee considering an outside directorship, a consulting arrangement, or an investment can ask before acting, and receive a clear answer from the right reviewer.
This changes how staff experience the process. Instead of a yearly exercise that feels designed to catch them out, conflict management becomes a source of advice when they need it. People tend to engage with a process that helps them avoid problems, and that engagement produces more honest disclosures.
Spreadsheets Reach Their Limit
Running all of this manually is possible in a small organisation. It becomes unwieldy as headcount grows. Compiling staff lists, emailing forms, chasing non-responders, removing leavers, and adding new starters consumes a surprising amount of time, and people slip through the gaps.
This is where conflict of interest disclosure management software has become common. Connected to HR records, such systems can send the right form to the right people automatically, enrol new starters, update forms when someone changes role, schedule reminders, and show completion rates as a campaign runs. Declarations that need closer attention can be escalated into an investigation process, with the link back to the original disclosure preserved.
Technology does not decide whether a conflict is acceptable. Reviewers still need to weigh the circumstances, agree sensible safeguards, and record their reasoning. What automation removes is the administrative work that crowds out that judgement.
Getting The Basics Right
Whatever tools an organisation uses, a few principles tend to make the difference.
Policies should explain clearly what counts as a conflict, with practical examples drawn from the organisation’s own work.
Questions should match the risks attached to each role rather than applying a single template to everyone.
Declarations should be possible at any time, not only during the annual campaign.
Reviews should end with a recorded decision and, where needed, a clear arrangement such as stepping away from a particular contract.
Leaders should declare their own interests visibly and promptly, since staff take their cue from the top.
Questions Worth Asking
Do current disclosure forms ask different questions of people with different levels of decision-making power?
How quickly would a new conflict be noticed if it arose midway through the year?
Can reviewers easily distinguish routine declarations from those needing urgent attention?
Do employees know they can ask for guidance before taking on an outside interest?
Conflicts of interest are a normal part of working life. The organisations that manage them well are not the ones with fewer conflicts, but the ones that hear about them early enough to deal with them sensibly.

Choosing a nursery school is an important milestone for families. For many children, it is their first regular experience of learning alongside other children, following a classroom routine, and spending time away from home. While early literacy and numeracy certainly matter, nursery education supports a much wider range of developmental skills.
Young children learn best when they feel secure, interested, and actively involved. A thoughtfully designed nursery environment combines stories, play, conversation, movement, creativity, and practical experiences so children can develop naturally while enjoying the learning process.
Why Nursery Education Matters
The early years are a period of rapid growth. Children are developing language, coordination, social awareness, emotional regulation, and problem-solving abilities at the same time.
A nursery school can support these areas through everyday experiences rather than relying only on formal lessons.
For example, building with blocks involves planning and spatial awareness. Listening to stories develops vocabulary and comprehension. Playing with classmates introduces cooperation and communication.
Learning Happens Through Experience
Young children need opportunities to touch, move, build, sort, create, and experiment.
A good nursery school makes learning interactive. Instead of expecting children to absorb information passively, educators encourage them to explore concepts through activities that make sense at their developmental stage.
This helps children connect new ideas with real experiences.
Language Development Starts With Conversation
Children develop communication skills throughout the day.
Stories, songs, rhymes, role play, and everyday conversations expose children to new words and encourage them to express their ideas.
A nursery school should create many opportunities for children to speak, listen, ask questions, and participate in discussions.
Stories Encourage Imagination
Books do more than prepare children for reading.
Stories help children understand characters, emotions, sequence, and cause and effect.
Teachers can ask children to predict what happens next, describe illustrations, or talk about how a character might feel.
These interactions make literacy meaningful rather than mechanical.
Social Skills Grow in a Group Setting
Young children are still learning how friendships work.
They may struggle to share, wait for turns, or manage disagreements. These situations are normal and provide useful learning opportunities.
Families exploring a nursery learning environment in ESTZ Chennai can observe how educators help children communicate and cooperate.
A nursery school should guide children through social challenges without expecting perfect behavior.
Creativity Supports Flexible Thinking
Drawing, painting, music, construction, storytelling, and imaginative play give children opportunities to express themselves.
A nursery school should not make every creative activity produce an identical result.
Children benefit from choosing materials, experimenting with ideas, and discovering that there can be more than one way to solve a problem.
Mistakes Are Valuable
A tower may fall. A puzzle piece may not fit. A drawing may change halfway through.
These moments teach persistence.
Teachers can encourage children to try again rather than immediately completing the task for them.
Physical Development Needs Daily Attention
Young children need movement.
Running, jumping, balancing, dancing, climbing, and outdoor play support gross motor development. Drawing, threading, building, and puzzles strengthen fine motor control.
A balanced nursery school programme should include both energetic and quieter activities.
Movement can also improve concentration by giving children healthy opportunities to use their energy.
Independence Develops Gradually
Small responsibilities can build confidence.
Children might carry belongings, tidy materials, wash hands, select activities, or help organize a shared space.
A nursery school should allow children enough time to attempt manageable tasks independently while keeping adult support available.
These simple experiences teach children that they are capable.
Predictable Routines Create Security
Young children often feel more comfortable when the day follows a recognizable pattern.
Arrival, activities, meals, stories, movement, and departure cues help them anticipate what comes next.
Predictability can make the environment feel safe while children develop independence.
Conclusion
A nursery school provides much more than early academic preparation. It creates a community where children can build language, social confidence, creativity, physical coordination, emotional awareness, and independence.
The strongest early-learning experiences often happen during ordinary moments: listening to a story, solving a puzzle, completing a small task, or learning how to cooperate with a friend.
When children experience these moments in a warm and supportive environment, they develop skills and attitudes that can support them throughout their future education.

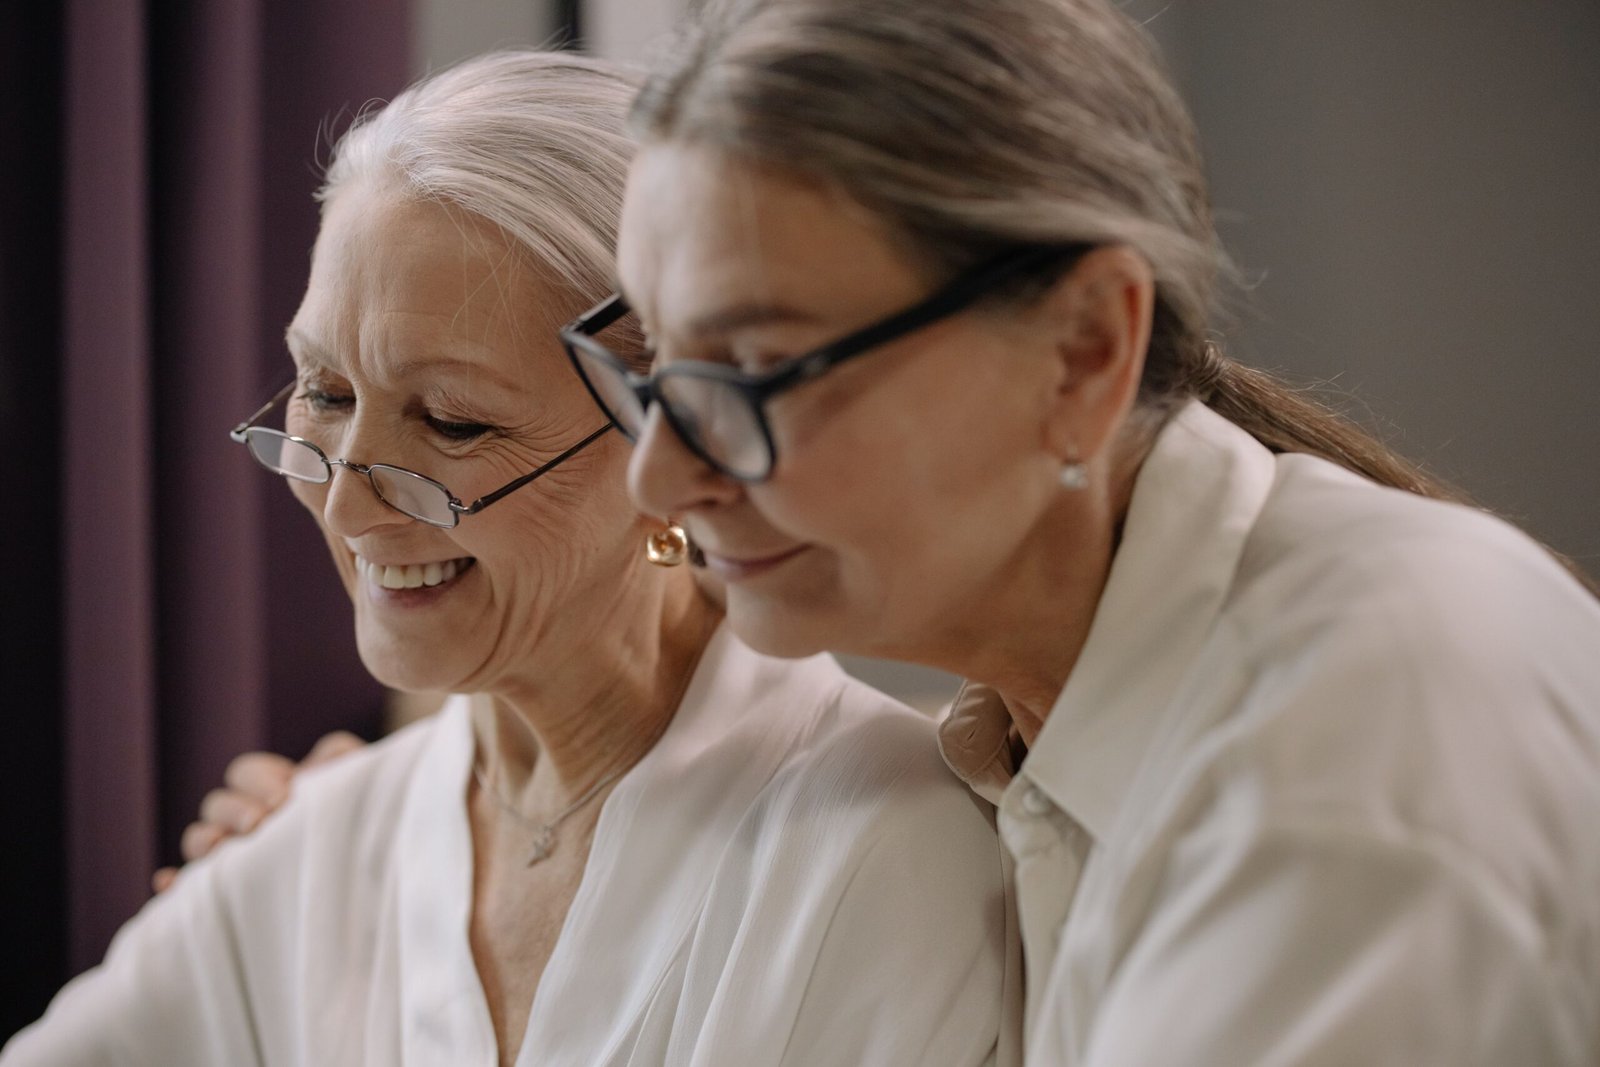
When aging adults consider moving to a senior living community, they are not simply looking for a place to eat and sleep. They are evaluating whether a community aligns with their values, respects their choices, and supports the lifestyle they want for the years ahead. What older adults want from senior living has changed considerably over time. Longer life expectancies, evolving family dynamics, and a desire for continued engagement have reshaped expectations. As a result, today’s senior living communities are adapting to meet a broader range of needs and preferences.
1. Independence and Autonomy in Daily Life
Aging adults consistently identify personal choice and independence as top priorities. They want the freedom to decide when to wake up, what to eat, and how to spend their time. Rather than following rigid schedules, many prefer communities that offer flexibility and support individualized lifestyles.
This desire for autonomy extends to personal wellness decisions as well. Many residents appreciate having a voice in how support services are provided, choosing the level of assistance that best fits their preferences and circumstances. Communities that offer flexible service options often help residents feel more comfortable, respected, and in control of their daily experiences.
2. Meaningful Social Connections and Community Engagement
Social connection plays an important role in overall well-being. While many older adults value their privacy, they also want opportunities to develop meaningful relationships and engage with others who share similar interests.
Residents often look for communities that offer book clubs, gardening groups, craft programs, educational discussions, and social gatherings. Beyond organized programs, they appreciate welcoming spaces where casual conversations and friendships can develop naturally.
Shared dining areas, community lounges, walking paths, and outdoor gathering spaces can help create an environment where relationships flourish. When residents feel connected to those around them, they often report greater satisfaction and a stronger sense of belonging.
3. Access to Quality Healthcare and Wellness Services
Reliable healthcare access remains an important consideration for many aging adults. Communities that coordinate wellness services, preventive care, and healthcare resources can provide valuable convenience and peace of mind.
Many seniors appreciate having access to wellness programs that focus on maintaining health and quality of life. These may include fitness classes, nutrition education, wellness seminars, and emotional well-being resources. Accessible healthcare services can help residents spend less time coordinating appointments and more time enjoying their daily routines.
The ability to easily access support when needed allows residents to feel confident as their needs change over time.
4. Affordability and Financial Transparency
Financial stability is a major consideration for many older adults. Residents want clear information about monthly costs, included services, and any additional fees. Transparent pricing helps families and residents make informed decisions without worrying about unexpected expenses later.
Families researching communities that balance affordability and quality often consider Taylor Place, an independent living community that helps prospective residents understand available services and pricing information. Communities that offer straightforward cost structures and a variety of service options can give residents greater flexibility when planning for the future.
When financial expectations are clear, residents can focus more on enjoying community life and less on concerns about unforeseen expenses.
5. Purpose, Learning, and Personal Growth Opportunities
Many outdated assumptions suggest that aging adults simply want to slow down during retirement. In reality, many seniors remain interested in learning, contributing, and pursuing personal interests.
Older adults often seek opportunities to attend educational programs, explore creative hobbies, learn new skills, and engage in meaningful volunteer work. Some communities partner with local organizations, colleges, and guest speakers to offer ongoing educational opportunities.
Many residents also enjoy sharing their experience and knowledge through mentoring, volunteering, and leadership opportunities within the community. These experiences provide a sense of purpose and reinforce the idea that personal growth can continue throughout every stage of life.
6. Privacy, Safety, and Personalized Support
Although community engagement is important, residents also value privacy and personal space. Aging adults often want apartments that reflect their personal style, opportunities to host family and friends, and quiet areas where they can relax and recharge.
Safety is another important consideration. Residents want confidence that community team members understand their needs and can provide appropriate support when necessary. Personalized service plans that incorporate resident input help ensure that support remains respectful and aligned with individual preferences.
Regular conversations about changing needs can help residents feel heard and empowered, contributing to a more positive living experience.
Conclusion
Senior living continues to evolve as aging adults seek communities that support far more than their basic daily needs. Today’s seniors want environments that respect their choices, encourage social connection, provide access to wellness resources, and create opportunities for continued growth and purpose. They also value transparency, privacy, and individualized support that recognizes their unique goals and preferences. Communities that embrace these priorities can create meaningful experiences that help residents remain engaged, connected, and fulfilled while enjoying the next chapter of life.

The Conflicts Nobody Thinks To Declare

How to Source European Bricks for UK Building Projects

How Automation is Reshaping the Global Food & Beverage Packaging Industry in 2026
Who Is Shameera? All You Need To Know About Charli XCX’s Mother
Who Is Gulliver Flynn Oldman? The Untold Story of Sir Gary Oldman’s Son
Meet Rosemary Turner: The Mother of Actor Callum Turner
-
Biographies8 months ago
Who Is Shameera? All You Need To Know About Charli XCX’s Mother
-
Biographies8 months ago
Who Is Gulliver Flynn Oldman? The Untold Story of Sir Gary Oldman’s Son
-
Biographies8 months ago
Meet Rosemary Turner: The Mother of Actor Callum Turner
-
 Biographies6 months ago
Who is Alexandra James? Inside The Life of Jeremy Clarkson’s Former Partner
-
 Biographies8 months ago
Who is Todd McRae? Meet Tate McRae’s Father
-
 Biographies7 months ago
Who Is Daniel Mara? The Untold Story of Kate Mara’s Private Sibling
-
 Celebrity8 months ago
Who Is Peter Hernandez? The Real Story of Bruno Mars’ Father
-
 Biographies8 months ago
Who Was Adrian Mayers? The Untold Life of A$AP Rocky’s Late Father